invisibletech.ai
What is Forward Deployed Engineering?
Forward deployed engineering embeds engineers in your environment to build AI systems that work in production. See how Invisible Technologies makes FDE scale.
João Paulo Carvalho

The links, tools and tips our engineers and designers share with each other, one “today I learned” at a time.
invisibletech.ai
Forward deployed engineering embeds engineers in your environment to build AI systems that work in production. See how Invisible Technologies makes FDE scale.
João Paulo Carvalho
Tech Insights· invisibletech.ai
From invisibletech.ai
Forward deployed engineering embeds engineers in your environment to build AI systems that work in production. See how Invisible Technologies makes FDE scale.
Shared by
performance.dev
breakdown of the architecture behind Linear's speed: local-first sync, MobX observables, instant first loads, and a keyboard-first design.
Raí Siqueira
Tech Insights· performance.dev
From performance.dev
breakdown of the architecture behind Linear's speed: local-first sync, MobX observables, instant first loads, and a keyboard-first design.
Shared by
cursor.com
Canvases let Cursor render dashboards and custom interfaces as interactive artifacts alongside the chat.
Lucas Vilela
Tech Insights· cursor.com
From cursor.com
Canvases let Cursor render dashboards and custom interfaces as interactive artifacts alongside the chat.
Shared by
newsletter.getdx.com
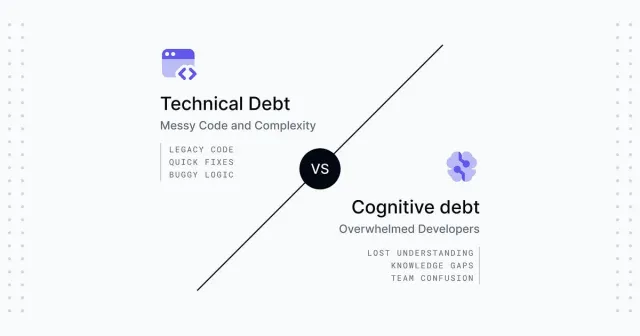
How cognitive debt shows up in practice and early mitigation strategies.
Ricardo Morato Rocha
Tech Insights· newsletter.getdx.com
From newsletter.getdx.com
How cognitive debt shows up in practice and early mitigation strategies.
Shared by
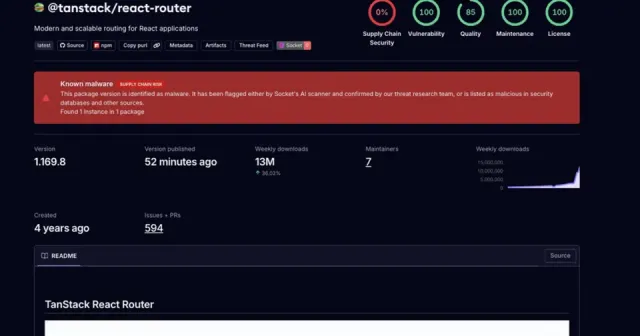
socket.dev
Raí Siqueira
Tech Insights· socket.dev
Shared by
aicoding.leaflet.pub
Ricardo Morato Rocha
Tech Insights· aicoding.leaflet.pub
Shared by
paperdraw.dev
Build system architecture diagrams, run traffic simulations, and inject chaos events in one system design tool.
Hernany Costa
Tech Insights· paperdraw.dev
From paperdraw.dev
Build system architecture diagrams, run traffic simulations, and inject chaos events in one system design tool.
Shared by
praetorian.com
Recently, we identified several critical Pwn Request vulnerabilities within GitHub Actions used by the Rspack repository. These vulnerabilities could allow an external attacker to submit a malicious pull request, without the requirement of being a prior contributor to the repository, and compromise the following secrets...
Gabriela Cavalcante
Tech Insights· praetorian.com
From praetorian.com
Recently, we identified several critical Pwn Request vulnerabilities within GitHub Actions used by the Rspack repository. These vulnerabilities could allow an external attacker to submit a malicious pull request, without the requirement of being a prior contributor to the repository, and compromise the following secrets...
Shared by
Tech Insights· github.com
Shared by
attackshipsonfi.re
TL;DR The Google developer documentation includes CSP examples which use domain wildcards (which have been widely cut & pasted), and additionally there are numerous endpoints within the Google eTLDs which are vulnerable to Javascript XSS.
Ricardo Morato Rocha
Tech Insights· attackshipsonfi.re
From attackshipsonfi.re
TL;DR The Google developer documentation includes CSP examples which use domain wildcards (which have been widely cut & pasted), and additionally there are numerous endpoints within the Google eTLDs which are vulnerable to Javascript XSS.
Shared by
github.com
htop for your Claude Code sessions — real-time cost, cache efficiency, model comparison, and smart alerts - liorwn/claudetop
Lucas Vilela
Tech Insights· github.com
From github.com
htop for your Claude Code sessions — real-time cost, cache efficiency, model comparison, and smart alerts - liorwn/claudetop
Shared by
haskellforall.com
Specifications do not address the limitations of agentic coding
Vitor Rangel
Tech Insights· haskellforall.com
From haskellforall.com
Specifications do not address the limitations of agentic coding
Shared by
cruft.io
In this article, I share what I learned from improving the security-related response headers sent by our ExpressJS server.
Ricardo Morato Rocha
Tech Insights· cruft.io
From cruft.io
In this article, I share what I learned from improving the security-related response headers sent by our ExpressJS server.
Shared by
Book a call
Tell us about your product and the problem in front of you. We’ll bring what we’ve learned on real projects.
Tell us about your product, and we’ll bring what we’ve learned.
Still prefer the good old email? Contact us