Lessons about Security (page 5)
The links, tools and tips our engineers and designers share with each other, one “today I learned” at a time.
- lessons shared
- 68
- people sharing
- 19
- database started in
- 2016
Tech Insights· medium.com
Auto-incremented primary keys are not very safe, consider using uuid
Shared by
Read on medium.com- Database
- Security
github.com
BinaryAlert: Serverless, Real-time & Retroactive Malware Detection
BinaryAlert: Serverless, Real-time & Retroactive Malware Detection. - airbnb/binaryalert
Flávio Juvenal
Tech Insights· github.com
BinaryAlert: Serverless, Real-time & Retroactive Malware Detection
From github.com
BinaryAlert: Serverless, Real-time & Retroactive Malware Detection. - airbnb/binaryalert
Shared by
Read on github.com- Files
- Malware
- S3
- Security
Tech Insights· github.com
Process untrusted XML safely with defusedxml Python lib:
Shared by
Read on github.com- Security
- Xml
blog.codinghorror.com
Hacking your own password hashes to test security:
We’ve read so many sad stories about communities that were fatally compromised or destroyed due to security exploits. We took that lesson to heart when we founded the Discourse project; we endeavor to build open source software that is secure and safe for communities by default, even if there
Flávio Juvenal
Tech Insights· blog.codinghorror.com
Hacking your own password hashes to test security:
From blog.codinghorror.com
We’ve read so many sad stories about communities that were fatally compromised or destroyed due to security exploits. We took that lesson to heart when we founded the Discourse project; we endeavor to build open source software that is secure and safe for communities by default, even if there
Shared by
Read on blog.codinghorror.com- Password
- Security
ncsc.gov.uk
Let users paste passwords:
The contents were out of date or replaced, but you can still access the information via The National Archives website. Details how to do this below.
Flávio Juvenal
Tech Insights· ncsc.gov.uk
Let users paste passwords:
From ncsc.gov.uk
The contents were out of date or replaced, but you can still access the information via The National Archives website. Details how to do this below.
Shared by
Read on ncsc.gov.uk- Password
- Security
- Usability
docs.djangoproject.com
HTTPOnly flag on the session cookies helps to prevent XSSs from escalating to session hijack: #std:setting-SESSION_COOKIE_HTTPONLY
Flávio Juvenal
Tech Insights· docs.djangoproject.com
HTTPOnly flag on the session cookies helps to prevent XSSs from escalating to session hijack: #std:setting-SESSION_COOKIE_HTTPONLY
Shared by
Read on docs.djangoproject.com- Security
- Web
security.googleblog.com
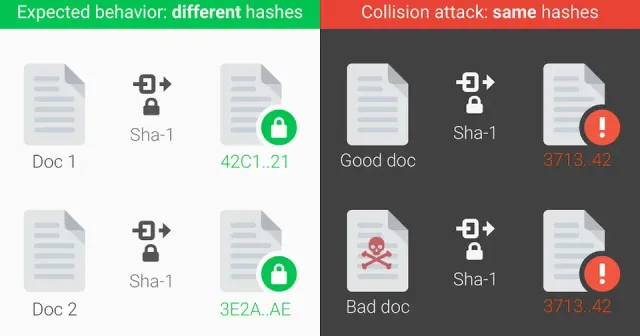
SHA1 first collision was generated. You should be using SHA256:
Posted by Marc Stevens (CWI Amsterdam), Elie Bursztein (Google), Pierre Karpman (CWI Amsterdam), Ange Albertini (Google), Yarik Markov (Goog...
André Ericson
Tech Insights· security.googleblog.com
SHA1 first collision was generated. You should be using SHA256:
From security.googleblog.com
Posted by Marc Stevens (CWI Amsterdam), Elie Bursztein (Google), Pierre Karpman (CWI Amsterdam), Ange Albertini (Google), Yarik Markov (Goog...
Shared by
Read on security.googleblog.com- Cryptography
- Security
github.com
Use this lib to estimate password strength in Python:
Python implementation of Dropbox's realistic password strength estimator - dwolfhub/zxcvbn-python
Felipe Farias
Tech Insights· github.com
Use this lib to estimate password strength in Python:
From github.com
Python implementation of Dropbox's realistic password strength estimator - dwolfhub/zxcvbn-python
Shared by
Read on github.com- Python
- Security
Book a call
Found it useful?
Let’s put it to work.
Tell us about your product and the problem in front of you. We’ll bring what we’ve learned on real projects.
Tell us about your product, and we’ll bring what we’ve learned.
Still prefer the good old email? Contact us